

As digital onboarding becomes more common, businesses are dealing with increasingly sophisticated identity fraud, including synthetic identities, manipulated documents, and deepfakes. Businesses once relied on a single ID check at signup, but now they require a more thorough verification process.
A single process doesn’t work for every customer. A shopper buying an age-restricted product and an overseas company opening a high-value account carry very different risks.
Treating them the same can either waste resources or leave gaps in the process.
Risk-based compliance solves this by matching the level of scrutiny to the level of risk associated with the customer or relationship. The core decision is knowing when standard customer due diligence (CDD) is enough and when enhanced due diligence (EDD) is necessary.
This guide explains how customer due diligence and enhanced due diligence work, where each applies, and how modern technology makes both faster and more accurate.
- CDD (customer due diligence) is the standard baseline for verifying customers, while EDD (enhanced due diligence) is a deeper investigation reserved for higher-risk customers.
- Risk-based compliance means matching scrutiny to risk instead of running identical checks on every customer.
- Key rules include FinCEN’s CDD Rule, Section 312 of the USA PATRIOT Act, and FATF Recommendations. U.S. domestic BOI reporting under the Corporate Transparency Act ended in August 2026, but the CDD Rule still requires financial institutions to verify beneficial owners.
- The most common mistakes are mixing up sources of wealth and sources of funds, overapplying EDD, documenting decisions without reasoning, and treating EDD as a one-time task.
- Perpetual KYC, AI-driven fraud defenses, digital ID support, and automated ownership tracking are reshaping due diligence into a continuous, more accurate process.
What Is Customer Due Diligence (CDD)?
Customer due diligence (CDD) is the standard process businesses use to understand who their customers are and assess the risks associated with the relationship. It includes identifying a customer, verifying their identity, understanding the purpose of the relationship, and monitoring activity over time.
It applies to nearly every customer at onboarding and is usually enough for low- to medium-risk customers.
These are typically individuals with clear identity records, ordinary transaction patterns, and no red flags. Where regulations allow and risk is clearly low, some businesses use a lighter, simplified version of due diligence.
What Is Enhanced Due Diligence (EDD)?
CDD stands for customer due diligence, the standard identity and risk check for most customers. EDD adds deeper scrutiny, such as source-of-wealth and source-of-funds checks, when a customer poses higher risk.
Enhanced due diligence (EDD) is a deeper level of investigation applied when a customer presents higher risk.
Common triggers include politically exposed persons (PEPs), links to high-risk jurisdictions, complex ownership structures, unusually large or unexplained transactions, and adverse media.
EDD goes beyond identity checks. It examines the source of wealth, the source of funds, and business purposes, with closer ongoing monitoring and often senior management approval. In the CDD vs. EDD comparison, CDD is the baseline, while EDD is the escalation. Strong EDD compliance means applying it where risk demands it, not to every customer.
CDD vs EDD: Key Differences Explained
CDD and EDD serve different purposes within a risk-based due diligence process. While CDD establishes a baseline understanding of the customer and their risk, EDD adds deeper review when additional risk factors are present.
The table below highlights the key differences between the two:
| Factor | CDD | EDD |
|---|---|---|
| Purpose | Establish baseline customer identity and risk | Investigate and mitigate elevated risk |
| Customer scope | Most customers | Higher-risk customers or situations |
| Identity verification | Standard identity and verification checks appropriate to the customer and risk | Additional verification, corroborating data, and manual review where needed |
| Screening | Sanctions, PEP, and adverse-media checks | Deeper screening, investigation, and dispositioning |
| Beneficial ownership | Required for applicable legal-entity customers | More detailed ownership and control analysis |
| Transaction monitoring | Standard monitoring | Tighter thresholds, more frequent review, and enhanced investigation |
| Documentation | Standard risk assessment and records | Detailed rationale, approvals, source-of-funds/wealth evidence, and audit trail |
| Review frequency | Risk-based periodic review | More frequent, event-driven review |
CDD and EDD Across Key Industries
Due diligence expectations differ by sector because the laws, customers, and risks differ. Here is how CDD and EDD typically play out in three industries under close scrutiny.
FinTech & Banking
Banks, broker-dealers, and other covered financial institutions must run CDD on customers under the Bank Secrecy Act framework, including identifying beneficial owners of legal entity customers.
EDD applies to higher-risk profiles such as Politically Exposed Persons/PEPs, correspondent banking relationships, and customers in high-risk jurisdictions.
Fintechs that operate as money services businesses or partner with a bank face the same expectations, directly or through their bank partner.
Customer due diligence solutions that combine document verification, sanctions and PEP screening, and continuous monitoring help these teams onboard quickly without missing risk signals.
Ecommerce & Age-Restricted Retail
Most ecommerce retailers aren’t covered financial institutions, so the federal CDD Rule doesn’t apply to them directly.
Due diligence still matters. Merchants selling tobacco, vape, alcohol, or CBD must verify age, and payment processors often apply their own underwriting and enhanced review to higher-risk merchant categories.
CDD here may include identity and age verification, address and payment checks, and fraud screening at checkout.
EDD may apply to unusually large orders, reshipping patterns, or accounts showing signs of synthetic identity fraud or account takeover.
Online Gaming & Gambling (iGaming)
Gambling operators face strict verification demands.
Certain U.S. casinos and card clubs that meet applicable Bank Secrecy Act requirements are covered financial institutions, while state and international gaming regulators may also require age and identity verification before a player can wager.
CDD covers identity, age, location, and self-exclusion checks at signup.
EDD typically applies to high-value players, unusual deposit patterns, or PEP matches, with source-of-funds and source-of-wealth checks where required by applicable rules or risk procedures.
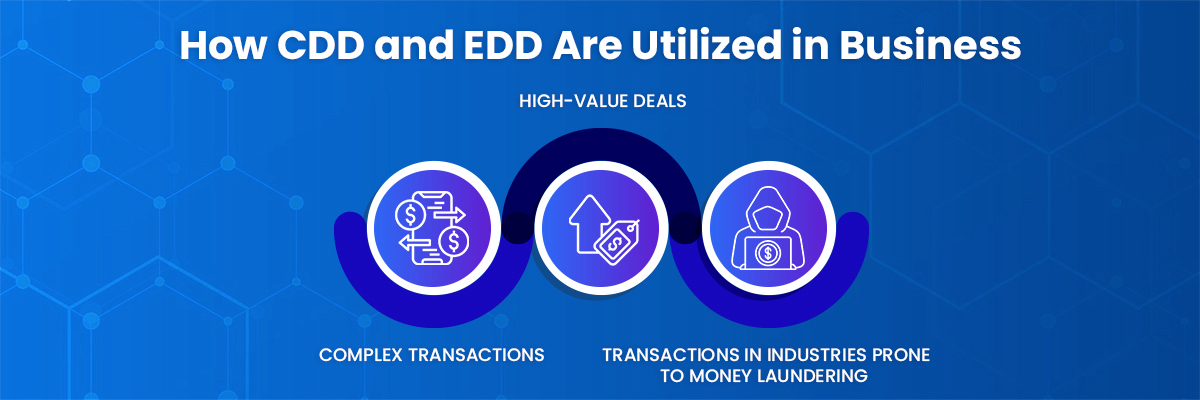
How CDD and EDD Are Utilized in Business
CDD forms the basis of customer risk assessment and is applied to the majority of customers in various industries.
It’s a preliminary step that helps in categorizing customers based on their risk profile, allowing businesses to conduct standard transactions with a reasonable level of assurance.
On the other hand, EDD is deployed when dealing with customers posing higher risks.
The focus here is on gathering more extensive information to mitigate those elevated risks effectively.
EDD is necessary for:
- Complex transactions
- High-value deals
- Transactions in industries prone to money laundering
Key Regulators and Rules That Govern CDD and EDD
Several bodies and rules shape what CDD and EDD must include.
Which ones apply depends on your industry and where you operate, so treat this as a map, not legal advice.
FinCEN and the CDD Rule
FinCEN’s (Financial Crimes Enforcement Network) CDD Rule requires covered financial institutions such as banks, broker-dealers, mutual funds, and futures commission merchants to meet four core requirements:
- Identify and verify customers.
- Identify and verify the beneficial owners of legal entity customers.
- Understand the nature and purpose of each relationship to build a risk profile.
- Monitor accounts on an ongoing basis.
The rule sets the baseline for CDD, while EDD is triggered by a customer’s risk rating and by other rules, such as Section 312.
Section 312 of the USA PATRIOT Act
Section 312 requires covered U.S. financial institutions to run due diligence on correspondent accounts and private banking accounts held for non-U.S. persons.
It mandates enhanced due diligence for correspondent accounts of certain foreign banks, such as those operating under an offshore license or licensed in jurisdictions designated as non-cooperative or as warranting special measures.
For private banking accounts with at least $1 million in deposits, it requires enhanced scrutiny of accounts held by senior foreign political figures.
FATF Recommendations
The Financial Action Task Force (FATF) sets the global anti-money laundering standards that most countries build their laws around.
Recommendation 10 covers customer due diligence, Recommendation 12 addresses politically exposed persons, and Recommendation 19 calls for enhanced due diligence for relationships tied to higher-risk countries.
Recommendations 24 and 25 push for transparency about who owns and controls legal entities.
FATF standards aren’t legally binding on their own, but countries are evaluated against them, so their expectations show up in local rules.
Beneficial Ownership Information (BOI) Reporting
Beneficial ownership rules changed significantly in 2026.
A FinCEN final rule effective August 14, 2026, permanently exempts U.S. companies and U.S. persons from reporting beneficial ownership information under the Corporate Transparency Act.
Foreign entities registered to do business in the U.S. still report, but only for foreign individuals, and FinCEN will delete previously reported information from U.S. persons.
What didn’t change is the CDD Rule. It remains in effect and still requires covered financial institutions to identify and verify beneficial owners of their legal entity customers, and FinCEN has said it intends to modify the rule.
With U.S. companies no longer required to report BOI to FinCEN, financial institutions still need processes for identifying and verifying beneficial owners when required under the CDD Rule.
In February 2026, FinCEN issued an exceptive relief order allowing covered financial institutions to limit beneficial owner identification and verification to three situations: when a legal entity customer first opens an account, when the institution learns facts that reasonably call into question previously obtained information, or when its risk-based ongoing CDD procedures require it.
U.S. companies no longer have to file beneficial ownership reports with FinCEN, but financial institutions must still verify beneficial owners under the CDD Rule.
Common Pitfalls to Avoid in CDD & EDD Management
Even mature programs stumble on the same handful of mistakes.
Avoiding them protects both compliance and customer experience.
1. Conflating Source of Wealth (SoW) with Source of Funds (SoF)
Source of Wealth describes how a customer accumulated their overall wealth, while Source of Funds explains where the money for a specific transaction came from.
Confusing the two can lead to weak documentation and audit findings. Depending on the customer’s risk profile, businesses may need to establish both.
2. Over-Applying EDD
Sending too many customers through EDD slows onboarding, raises costs, and pushes legitimate customers away.
It also buries analysts in false positives, so real risks get less attention. Set clear risk criteria and reserve EDD for customers who actually meet them.
3. Documenting Outcomes Without Reasoning
Recording “approved” or “rejected” isn’t enough.
Regulators and auditors want to know why, including which risk factors were considered and how they were weighed.
Capture the rationale, the evidence reviewed, and the approver for every high-risk decision. Digital verification records make this easier to keep consistent.
4. Treating EDD as a One-Time Task
Risk changes over time. A customer may become a PEP, move to a high-risk jurisdiction, or change transaction behavior.
Schedule periodic reviews for high-risk customers and trigger extra reviews when events occur, rather than treating EDD as a box ticked at onboarding.
Write down why, not just what. Record which risk factors drove each high-risk decision and who approved it. A clear rationale is what holds up in an audit.
Due Diligence Trends: How Technology Is Redefining CDD and EDD
Technology is moving due diligence from paperwork to continuous, data-driven workflows.
Modern verification and compliance tools can help bring these processes together while allowing businesses to scale their level of scrutiny based on risk.
1. From Periodic KYC to Perpetual KYC (pKYC)
Traditional programs refresh customer files every first, third, or fifth year depending on risk.
Perpetual KYC replaces the calendar with continuous monitoring, updating a customer’s profile when something changes, such as a new sanctions listing, an adverse media hit, or an ownership change.
2. AI-Driven Fraud Countermeasures in Onboarding
Fraudsters now use generative AI to create synthetic identities, forged documents, and deepfakes.
Defenses are adapting with document forensics, liveness detection, injection attack detection, and device intelligence, helping businesses identify potentially manipulated or fraudulent onboarding attempts.
3. Interoperability with Digital ID Wallets & mDLs
Mobile driver’s licenses and digital ID wallets are spreading across U.S. states, and the EU is rolling out digital identity wallets under eIDAS 2.0.
Due diligence tools need to verify credentials securely alongside physical IDs, without adding friction for the customer.
4. Automated Beneficial Ownership Tracking
With domestic BOI reporting gone, firms need their own way to map who owns and controls legal entity customers.
Automated tools pull from company registries, resolve ownership chains, and flag changes, replacing manual spreadsheets and repeated document requests.
5. Regulatory Harmonization
Regulators are moving toward more consistent standards.
The European Union (EU) is building a single anti-money laundering (AML) rulebook and a new AML Authority, and the Financial Action Task Force (FATF) continues to align countries’ expectations.
For global businesses, this should eventually mean fewer conflicting local rules, though real differences will remain for years.
Wrapping Up
CDD establishes the foundation of customer verification. It confirms who a customer is, builds a risk profile, and sets the baseline for monitoring.
Identity verification is an important component of CDD, while EDD adds deeper investigation when higher risks appear. EDD works best when it’s reserved for the customers who truly need it.
The lesson from any CDD vs. EDD comparison is the same: businesses need flexible, risk-based programs, not identical checks for every customer.
Modern technology makes that practical. Identity verification and other customer due diligence solutions can help improve accuracy, detect potential fraud, and streamline compliance workflows, so teams spend their time on real risk instead of paperwork.
Build a due diligence process that scales with risk. See how FTx Identity brings ID validation, biometric checks, and audit-ready records into one platform, and request a free demo.